Contact

Security & Identity

Identity done right. Most breaches start with identity: a home-grown login, a shared password, a token that never expires. We design access the way the platforms do it, and we review the rest of the system with the same care.
Talk about Security & Identity

Problems we solve.

  • A login system someone wrote years ago and nobody dares to change.
  • Ten internal tools, ten passwords, no single sign-on.
  • No passkeys, no multi-factor, no way to revoke access quickly.
  • A GDPR posture that exists on paper and nowhere else.
  • No security review before go-live, and no secure development lifecycle after it.
  • A public-facing system that has never been threat-modelled.

What we deliver.

Packages with a defined scope and a typical duration. Each ends with something you keep.

4 to 8 weeks

Identity and access design

OpenID Connect, OAuth 2, single sign-on and passkeys across your systems, with a migration path off the legacy login.

3 to 6 weeks

.NET identity and platform hardening

ASP.NET Core identity, token lifetimes, secrets, dependency and configuration review, done by someone who works on the platform itself.

2 to 4 weeks

Zero-trust and security review

Threat model, findings ranked by real risk, and fixes sequenced so the important ones ship first.

3 to 5 weeks

Secure development lifecycle

Review gates, dependency scanning, secret management and training so the next release is as safe as this one.

How it fits.

Identity and access flow with zero-trust checks People + devicespasskeys · MFA · posture Identity providerOpenID Connect · SSO · Entra API gatewaytoken check · policy Services.NET · data short-lived tokens Audit logevery sign-in · every grant Secrets + keysscoped · rotated Review gatesecure SDLC Zero trust: every request verified, every grant recorded, nothing implicit
Sign-in goes through a standards-based identity provider, every API call is checked at the gateway with short-lived tokens, and grants, secrets and releases are all recorded and reviewed.

The stack.

  • OpenID Connect and OAuth 2
  • ASP.NET Core Identity
  • Microsoft Entra
  • Passkeys and WebAuthn
  • Zero-trust networking
  • Cloudflare Access
  • Threat modelling
  • OWASP ASVS

Why ZoneTech

Proof, not promises.

Our founder is a principal software engineer on Microsoft's .NET identity and security platform, the same stack that protects a large share of the world's enterprise applications. That is the bar we apply to yours.

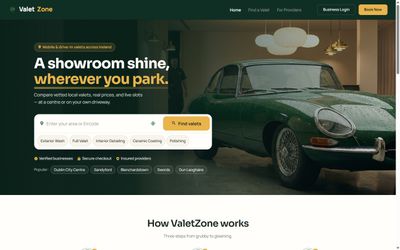
ValetZone

Smart parking and valet management with predictive availability, in Ireland.
  • Mobility
  • Predictive AI
  • Ireland
ValetZone screenshot

Start the conversation.

Tell us about the system and the constraint. We reply within two business days.

Contact ZoneTech